Rob van Eijk returns to hosts Jon Lebkowsky, Scoop Sweeney, and Wendy M. Grossman, starting from his policy report on pseudonymised and anonymous data, written with Benjamin de Vanssay. He explains why Europe protects privacy as a fundamental right while the US relies on consumer protection, and how data protection authorities investigate and gather evidence. On consent, he notes that the Global Privacy Control works in California because the law backs it, which Do Not Track never had. On AI, he favours narrow, purpose-built models over large general ones. The talk moves on to data centres, digital sovereignty, and open source. It ends on whether Trump v. Slaughter threatens the EU-US Data Privacy Framework, a question he leaves to the experts.
Computers, Privacy & Data Protection Conference (CPDP2026), Brussels
Marco Bassini of Tilburg University moderates a CPDP 2026 panel on the role of operating systems in trusted AI, centred on interoperability under DMA Article 6(7). Alba Ribera Martínez argues that the Commission's specification decisions erode GDPR and security safeguards. Gary Davis of Apple lists what the Commission asks of Android, from hotword waking to live microphone, contacts, and screen access, and calls each a new attack surface. Karina Nimara of the Developers Alliance warns that bad actors will exploit unlimited access and that apps would compete for finite battery and processing power. Sebastião Barros Vale of the EDPS insists that the DMA leaves the GDPR intact, with OS providers and apps as separate controllers. Rob van Eijk explains the layered, sandboxed design of a phone OS and asks who consents when a user delegates decisions to an AI agent. Several panelists want the EDPS, ENISA, and independent experts to join DG Competition in this work.
Rob van Eijk moderates a Data Protection Day 2026 panel on whether the Digital Omnibus proposal keeps pace with online tracking. Itxaso Domínguez de Olazábal of EDRi argues that the proposal treats ePrivacy as an obstacle to business and weakens the protection of devices under Article 5(3). Rosa Barcelo of McDermott Will & Emery finds it quite well balanced, an evolution rather than a revolution. She does see a gap between browser consent signals and the GDPR's granular consent. Cristiana Teixeira Santos of Utrecht University shows how server-side tracking and Unified ID 2.0 move beyond cookies, and finds that consent management platforms often fail to pass refusals on to third parties. Several panelists name weak enforcement as the main gap.
10 Years of Brussels Privacy Hub – What's Next, Brussels, 2025
For the Brussels Privacy Hub's tenth anniversary, Rob van Eijk gives a short expert view on where AI is heading. He is watching two developments. Agentic AI hands decisions over to software agents, and neuro-symbolic AI adds step-by-step reasoning so that AI can act as a coach or mentor. Both, he says, raise new privacy questions about user autonomy and loss of control. They lead him to a broader question about what it will mean to be human as society embraces these technologies.
Moderator, Computers, Privacy & Data Protection Conference (CPDP2025), Brussels
Rob van Eijk moderates a CPDP 2025 panel on why the adoption of privacy-enhancing technologies lags, and how governments can help. Sarah Holland of Google names organisational, technical, and cost barriers. She asks regulators for three incentives: a workable definition of anonymisation, credit for privacy-protective sharing, and PETs as a factor in the legitimate interest balancing test. Christian Reimsbach-Kounatze of the OECD points to cost, skills, and awareness, especially for SMEs, and to the OECD's work on a global repository of use cases. Valda Beizitere of the European Commission presents the EU digital identity wallet and privacy-friendly age verification as public building blocks. Van Eijk closes with a call to quantify risk and the effectiveness of PETs, so that anonymisation stops being an all-or-nothing question.
Computers, Privacy & Data Protection Conference (CPDP2024), Brussels
Cecilia Álvarez of Meta moderates a CPDP 2024 panel on the EU strategy for data, seen through AI and data protection. Rob van Eijk sets out how the data strategy, the DMA, the DSA, and the AI Act fit together, including Article 6(11) of the DMA and the AI Act timeline. Patricia Vidal, a competition lawyer, explains that dominance is not abusive in itself and that charging a fee is not abusive per se. Luca Bolognini calls for balancing rights with proportionality and practical rationality, and questions the EDPB's generic opinion on pay or consent. Peter Craddock argues that data protection reads necessity more strictly than contract law and that regulators overlook business realities. On pay or consent, Van Eijk applies proportionality and asks for alternatives for users who cannot pay.
Films & Politics #01 – "The Click Trap" Film Screening (Belgian Premiere) & Panel Discussion, Brussels, 2024
Rob van Eijk joins MEPs Brando Benifei and Francisca Hortal Foronda for a panel on digital regulation at the EU level, moderated by Kait Bolongaro. The panel follows the Belgian premiere of The Click Trap, a documentary about how digital advertising and micro-targeting fuel disinformation and threaten democracies.
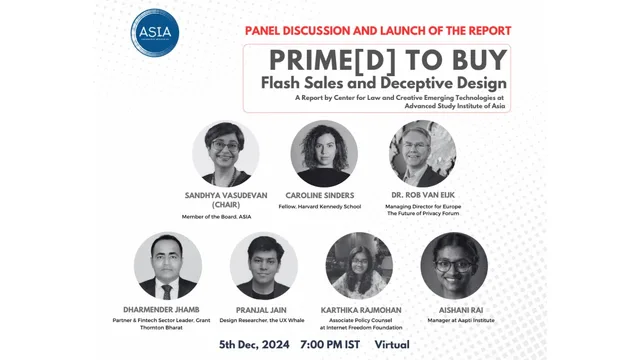
The Advanced Study Institute of Asia (ASIA) launches its report Prime[d] To Buy on flash sales and deceptive design. Its researchers found deceptive patterns in all 26 Indian apps they studied, about five per app. They also found inflated discounts and Apple users paying more than Android users. Vasudevan then chairs a panel. Jhamb of Grant Thornton points to missing detection tools and audits. Rai of the Aapti Institute raises micro-targeting and the loss of trust, and Rajmohan of the Internet Freedom Foundation the weak enforceability of India's 2023 guidelines on dark patterns. Rob van Eijk explains how the EU's DMA and DSA address deceptive design, and how enforcement is changing cookie banners and consent flows on large platforms.
In a short interview at the EDAA Summit 2023, Rob van Eijk asks regulators to learn more about how advertising technology works, including the limits and opportunities of the APIs now in play, so they can assess the impact on people's rights and freedoms. Privacy principles must keep up with a changing ecosystem, he says. That means understanding the data flows that web services create along the whole value chain.
In this EDAA Summit 2023 highlight reel, Rob van Eijk appears at 1m51s. He argues that a self-regulation framework "in today's day and age needs to have teeth". Demonstrating this capability, he says, is the most critical challenge for keeping self-regulatory frameworks in digital advertising relevant.
Jules Polonetsky of FPF hosts Rob van Eijk and Tobias Judin of the Norwegian DPA on the EDPB decision that extends Norway's ban on Meta's behavioural advertising across the EEA. Judin explains that Norway used the GDPR's urgency procedure, part of the one-stop-shop rules, because Meta kept processing unlawfully after the Irish orders. He stresses that legitimate interest is not dead and that the ban is limited to behavioural advertising. Van Eijk weighs the balancing test and points to the pending CJEU case C-621/22 on purely commercial interests. He sees ad tech moving from open real-time bidding to closed systems. On pay or okay, Judin calls it a case-by-case question of whether users can choose freely.
Rob van Eijk of FPF joins hosts Jon Lebkowsky, Scoop Sweeney, and Wendy M. Grossman to discuss where online advertising is heading. He explains how real-time bidding shares unique identifiers among thousands of companies, and how Google's Topics and Protected Audience APIs aim to replace the third-party cookie by keeping data in the browser and adding noise. He contrasts US consumer law with the EU's GDPR and ePrivacy rules. Contextual advertising in the Netherlands and Norway, he notes, has proved profitable. He describes hyper-nudging, a term he coined with Grossman for generative AI that fine-tunes ads to individual behaviour in real time. He expects age checks under laws such as the DSA to push the web toward platforms that require strong identity.
Jules Polonetsky of FPF hosts Christina Michelakaki and Rob van Eijk on FPF's report on five years of GDPR Article 25, data protection by design and by default, which covers more than 160 cases. Michelakaki shows that DPAs disagree on whether Article 25 applies before any harm. The Austrian and Finnish DPAs waited for a breach or actual processing, while the Belgian DPA and the Irish DPC applied it to risk alone. She also cites the Hungarian DPA's fine on a bank that used emotion recognition on customer calls. Van Eijk discusses the Dutch DPA's fine on the OLVG hospital, which did not check access logs and lacked two-factor authentication inside its own network. He points to ISO 27000 and the Europrivacy seal under Article 42 as ways to show compliance.
Computers, Privacy & Data Protection Conference (CPDP2023), Brussels
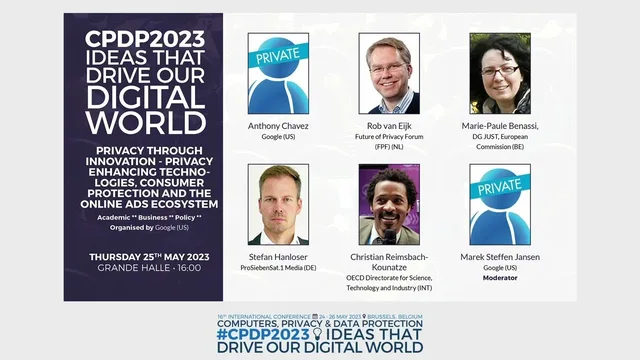
Marek Jansen moderates a CPDP 2023 panel on whether privacy-enhancing technologies can reconcile online advertising with privacy. Anthony Chavez of Google presents the Privacy Sandbox, a set of purpose-built APIs that replace third-party cookies and combine on-device processing, secure enclaves, and differential privacy. Marie-Paule Benassi of the European Commission introduces the Cookie Pledge, which treats consent fatigue as a consumer protection issue. Stefan Hanloser of ProSiebenSat.1 argues that contextual advertising earns less than targeted advertising, and warns that the new APIs may favour large intermediaries. Rob van Eijk of FPF sees the APIs as a way to apply purpose limitation and data minimisation. He points to profitable contextual models and warns of AI-driven hyper-nudging. Christian Reimsbach-Kounatze of the OECD warns against PET hype and names cost, skills, and legal uncertainty as barriers.
Moderator, Computers, Privacy & Data Protection Conference (CPDP2023), Brussels
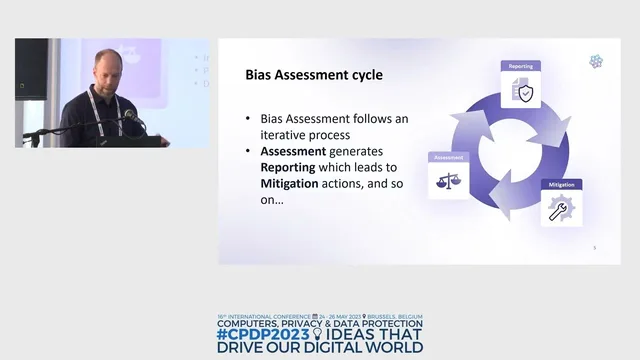
Rob van Eijk moderates a CPDP 2023 workshop on privacy-preserving machine learning, meant to help lawyers ask technologists the right questions. Lindsay Carignan and Nigel Kingsman of Holistic AI explain how they audit bias, with reference to New York City Local Law 144 and the EU AI Act. They contrast equality of outcome with equality of opportunity, show that reducing bias can cost accuracy and privacy, and list questions to ask data scientists. Victor Ruehle of Microsoft and Reza Shokri of the National University of Singapore turn to privacy risk. They use membership inference to measure how much a model leaks about its training data, with the open-source Privacy Meter. They also compare PII scrubbing with differential privacy, each of which trades some utility for privacy.
Nieuwsuur reporter Rudy Bouma investigates online advertising fraud, in which bots click on ads instead of people. Advertisers lose tens of billions a year. The item covers the Russian fraudster Aleksandr Zhukov, who ran servers in Amsterdam, and the dispute over the scale of the problem. The industry association VIA puts bot clicks at 1 to 2 percent, while TU Delft professor Michel van Eeten thinks the real figure is 10 to 30 times higher. Rob van Eijk, who wrote his PhD on real-time ad auctions, also expects the true number to be much higher because detection software misses many bot clicks. He concludes that cybercriminals have the upper hand.
Bianca-Ioana Marcu, managing director of CPDP, presents the 15th edition in 2022, back in person in Brussels, with more than 90 panels under the theme Data Protection and Privacy in Transitional Times. Leonardo Cervera-Navas of the EDPS argues that technological progress without proper regulation is pointless. Gloria González Fuster previews Privacy Camp's session and the first in-person meeting of the Data Protection Law Scholars Network. Rob van Eijk introduces FPF's masterclass on privacy-enhancing technologies and a panel on sharing mobility data. Thierry Vandenbussche previews the Privacytopia arts festival, and Jelle Hoedemaekers presents AI4Belgium's session on children and AI. Paul De Hert describes Brussels as a capital of technology regulation.
Jules Polonetsky of FPF hosts Jonas Breuer and Ine van Zeeland of SMIT at VUB, with Rob van Eijk, on their Data Walks project. The researchers took more than 100 citizens on 14 walks past cameras, sensors, and smart bins in three Belgian cities. Most people never notice information signs, they found, and people want to know why a city collects their data. The walks also surface concerns that a desk-based DPIA would miss. Van Eijk points to Amsterdam's online sensor map and to privacy-friendly designs in Rotterdam, such as infrared sensors that count waiting cyclists and cameras that turn people into wireframes. Cities usually rely on public interest, he notes, because consent is impractical in public space.
ADM case law Report: roundtable discussion, Brussels, 2022
Rob van Eijk opens and Gabriela Zanfir-Fortuna moderates an FPF roundtable in Brussels on the FPF report on automated decision-making. Co-author Sebastião Barros Vale presents findings from more than 70 court and DPA decisions. The GDPR governs automated decisions well beyond Article 22, he finds. The Article 22 threshold itself is high, and enforcers interpret it differently, as in the Uber, Ola, and Clearview AI cases. Mireille Hildebrandt of VUB notes that trade secrets do not block an explanation of the parameters behind a score. Gianclaudio Malgieri of the Brussels Privacy Hub asks why gig workers see different outcomes and why data subjects carry the burden of proof. Brendan Van Alsenoy of the EDPS calls Article 22 a rule rather than a standard and sees a role for sector-specific rules, such as the platform work directive.
Moderator, Computers, Privacy & Data Protection Conference (CPDP2022), Brussels
Rob van Eijk moderates a CPDP 2022 panel on whether the EU Mobility Data Space and the Data Act can serve the common good. Maria Rosaria Coduti of DG CONNECT presents the data strategy, the Data Governance Act, and the Data Act, including data altruism, access rights to IoT data, and business-to-government data sharing. Laura Cerrato, a data protection officer in the Brussels public sector, points out that public bodies often lack a legal basis for smart mobility projects. Arjan Kapteijn of the Dutch DPA reports that cities often treat mobility data as non-personal and skip DPIAs. David Wagner of the German Research Institute for Public Administration argues that mobility data is very hard to anonymise and that the GDPR needs a measurable standard for anonymity. The panellists end by calling for clear anonymisation standards and citizen participation.
Moderator, Computers, Privacy & Data Protection Conference (CPDP2022), Brussels
Rob van Eijk moderates a CPDP 2022 masterclass that explains de-identification techniques to a non-technical audience. He frames it with Recital 26 and the risks of singling out, linkability, and inference. Sophie Stalla-Bourdillon of Immuta and the University of Southampton presents homomorphic encryption. Each PET gives different guarantees and needs a risk assessment per party, she argues, and they work best in combination. Naoise Holohan of IBM Research explains differential privacy, which adds calibrated noise and uses epsilon to measure privacy loss. Nobody has yet issued guidelines for choosing epsilon. Lucy Mosquera of Replica Analytics covers synthetic data: how to generate it, how to measure its privacy risk, and its uncertain regulatory status. For DPOs, the session's advice is to talk to data scientists early and ask them to explain their risk metrics.
CPRA Law + Tech Series: Understanding Data, Decisionmaking, and Design, Washington, DC, 2022
Tanvi Vyas of Mozilla and Rob van Eijk of the Future of Privacy Forum give the fifth session of the CPRA Law and Tech Series, hosted by Stacey Gray of FPF and Sheri Porath Rockwell of the California Lawyers Association. Van Eijk takes apart a display ad and the browser to show where cookies and other storage live. He also shows how Chrome, Firefox, and Safari differ in handling third-party cookies by default. Vyas traces opt-out cookies, the failure of Do Not Track without legal backing, and today's confusing consent banners. She presents the Global Privacy Control header and argues that it needs clear legal backing, because its enforceability under the CCPA is still ambiguous. Van Eijk gives two examples of machine-readable signals: the _nomap Wi-Fi opt-out from the Dutch DPA's Google Street View case, and noyb's Advanced Data Protection Control for consent and withdrawal under EU law. He ends by stressing that defaults and definitions both matter.
Nieuwsuur journalists Mirjam de Galan and Nathalie Lemoine interview Rob van Eijk about the proposed EU Digital Green Certificate, a pan-European credential for COVID-19 vaccination, test, or recovery status. They ask him to assess the privacy implications of the proposed regulation. The interview covers the personal data on the certificate and how verifiers would check it at borders and venues. It also asks whether the European Commission's approach offers enough data protection safeguards.
Jules Polonetsky of FPF hosts a book club on Privacy is Hard and Seven Other Myths by Jaap-Henk Hoepman of Radboud University. Hoepman explains that many systems can be built with far more privacy, though technology alone is not enough, and names the business model as the elephant in the room. Asked what he would fix first, he picks sender anonymity on the internet and interoperable messaging. Rob van Eijk links the book's account of IRMA to attribute-based credentials and asks whether privacy as control still fits centralised systems. Gloria González Fuster, Gwendal Le Grand, Katharina Koerner, and Naomi Lefkovitz see the book as a bridge between lawyers and engineers. They also discuss involving stakeholders early and the role of regulation when markets fail.
Jules Polonetsky and Rob van Eijk of FPF present an FPF infographic, led by Van Eijk, that maps the data flows behind two common situations: online retail and remote learning. Van Eijk shows how a retailer relies on a stack of cloud services, from hosting and analytics to customer support, SMS, and multi-factor authentication. Specialist vendors run each of them, with their own subcontractors. For online learning he adds edge caching, video classrooms, learning management systems, and single sign-on. Polonetsky sets this against the Schrems II judgment. Nobody can simply split services that run on globally intertwined stacks by geography, he argues, so safeguards have to start from how data actually flows.
In this Serious Privacy episode, Paul Breitbarth and K Royal share short interviews that Breitbarth recorded at the IAPP conference in Brussels, asking privacy professionals for their predictions, worries, and words of wisdom. Guests include Rob van Eijk and Gabriela Zanfir-Fortuna of the Future of Privacy Forum, Bojana Bellamy of CIPL, Estelle Massé of Access Now, Trevor Hughes of the IAPP, Alexander Hanff, Andreea Lisievici, Anna Pouliou, Aoife Sexton, and Caroline Olstedt Carlström. Topics include AI, using data for good, awareness of digital identities, children's privacy, Brexit, and joint enforcement.
1st International Workshop on Consent Management in Online Services, Networks and Things (COnSeNT 2021), Virtual
Vitor Jesus moderates a COnSeNT 2021 panel on whether consent works online and what could replace it. Armand Heslot of the CNIL states that a cookie banner with only an accept button does not give valid consent, because refusing must be as easy as accepting. Townsend Feehan of IAB Europe presents the Transparency and Consent Framework as a tool to comply with GDPR and ePrivacy. Robin Berjon of The New York Times calls the TCF a configuration string. He argues for needing less consent, for example by ruling out third-party controllers. Irene Kamara of Tilburg University calls letting users choose legitimate interest unlawful, and points to the Radio Equipment Directive to make standards binding. Mark Lizar argues for consent receipts that people keep themselves. Rob van Eijk explores privacy preferences set in browsers and devices.
Moderator, Computers, Privacy & Data Protection Conference (CPDP2021), Brussels
Rob van Eijk moderates a CPDP 2021 panel on why published privacy standards are slow to reach products and services, and how to close that gap. Clara Neppel of IEEE names three challenges: defining privacy, trade-offs between privacy and functionality, and the balance between governance and technical measures. She sees standardisation as a way to build consensus and trust. Paul Nemitz of the European Commission argues that democracy makes the rules and standards implement them. Privacy by design is already law, he says, and the gap lies in enforcement. Mikuláš Peksa MEP argues for decentralised, interoperable architectures that no single company controls. Amelia Andersdotter of dataskydd.net points to the missing middle between legal principles and technical detail, and asks procurers and DPOs to use the standards that already exist.
Rob van Eijk moderates an FPF Dublin Privacy Symposium on interfaces that are transparent and do not manipulate. Graham Carroll of Friday Agency reports that 92% of visitors accepted cookies when the banner offered only accept and manage, and 85% when it added reject. Lorrie Cranor of Carnegie Mellon University tested icons for California's privacy options. Icons need text, she shows, and every change needs new testing. Hanna Schraffenberger of Radboud University finds that people agree to share data even when nudged to disagree. Daragh O'Brien of Castlebridge raises accessibility for colour-blind users. Diarmaid Mac Aonghusa of Fusio says the consent system fails people who click out of frustration. Dylan Corcoran of the Irish DPC asks organisations to test whether users understand. Denis Kelleher of LinkedIn and Stacey Gray of FPF place transparency in governance and US consumer protection law.
Moderator, 11th Annual European Data Protection & Privacy Conference, Brussels, 2021
Rob van Eijk moderates a Forum Europe panel at the 11th Annual European Data Protection and Privacy Conference on artificial intelligence and data spaces for the public good. Speakers Damian Clune, Cornelia Kutterer of Microsoft, Daniel Leufer of Access Now, Cristina Álvarez Rigaudias, and Christian D'Cunha examine the privacy implications of a data-sharing economy. The panel addresses how data spaces enabling AI development must be designed with strong data protection safeguards, how consent and purpose limitation apply when data is pooled across sectors, and how regulators can ensure that public-benefit data spaces do not become vehicles for commercial surveillance.
Ministerie van Volksgezondheid, Welzijn en Sport, Den Haag, 2020
Rob van Eijk takes part as an invited privacy expert in the Appathon that the Dutch Ministry of Health held in April 2020 to assess proposed coronavirus contact tracing apps. The ministry had received over 750 proposals and shortlisted seven. About 67 independent experts in privacy, security, epidemiology, and ICT evaluated them. Van Eijk comments on the privacy and data protection aspects of the shortlisted apps.
Jules Polonetsky of the Future of Privacy Forum hosts a LinkedIn Live roundtable, 2021 U.S. Privacy Landscape: Update for Global Stakeholders, on what the new US Administration and Congress mean internationally for privacy and data protection. He is joined by Jonathan M. Baron of Baron Public Affairs, a policy and political risk strategist. FPF's global and Europe leads, Gabriela Zanfir-Fortuna and Rob van Eijk, complete the panel.
Jules Polonetsky of the Future of Privacy Forum hosts a LinkedIn Live, EU Data Protection Chiefs: Schrems II Guidance Update, a week after the Court of Justice's Schrems II judgment. He is joined by Rob van Eijk and Gabriela Zanfir-Fortuna of FPF, Caitlin Fennessy of the IAPP, Andrew Serwin of DLA Piper, and Paul Breitbarth of TrustArc. They discuss the European Data Protection Board's answers to frequently asked questions on the judgment, and first reactions from DPAs, companies, the US government, and data protection scholars.
Jules Polonetsky of FPF hosts a book club with Michael Kearns and Aaron Roth of the University of Pennsylvania on The Ethical Algorithm. The authors argue that the problems algorithms cause need, in large part, algorithmic solutions, with privacy and fairness built into the models. They present differential privacy as a mature, rigorous definition. Fairness research, they say, is some fifteen years behind, with competing definitions that cannot all hold at once. Rob van Eijk asks whether humans can stay in the loop. The authors answer that human oversight is necessary but not sufficient at scale. Other questions cover contact tracing, interpretability, and how to test for bias when the GDPR limits collecting sensitive data.
Hadda Yadine and Ricky Groen of the Fons Vitae Lyceum in Amsterdam interview Rob van Eijk for their profielwerkstuk, a secondary school research project, on whether privacy on the internet still exists at all.
Moderator, Future of Privacy Forum and Dataskydd.net webinar, Washington, DC, 2020
Rob van Eijk moderates a joint FPF and dataskydd.net webinar on privacy in high-density crowds and Wi-Fi networks. Amelia Andersdotter explains why privacy-preserving standards reach EU policy and public procurement slowly. Jerome Henry of Cisco presents IEEE P802E, a framework that helps engineers assess and limit what Wi-Fi and other 802 protocols reveal about devices. Marit Hansen of the Schleswig-Holstein DPA warns that cars and phones now act as access points. She proposes using the locally administered bit of MAC addresses to signal which ones collectors may record. Jelena Burnik of the Slovenian DPA sees the GDPR as the source of demand for such standards and wants DPAs involved in drafting them. Udo Oelen of Dutch Railways explains how NS hashed Wi-Fi data twice and kept travel patterns for one day only. NS stopped once it no longer needed the data. Tiago Rodrigues of the Wireless Broadband Alliance and Kelsey Finch of FPF also contribute.
Moderator, Computers, Privacy and Data Protection Conference (CPDP2020), Brussels
Rob van Eijk moderates a CPDP 2020 panel on the algorithmic regulation of transport. Karen Vancluysen of the POLIS network argues that cities must regulate new mobility services so they serve public goals such as safety and clean air. Cities should first ask what data they actually need. Kara Selke of StreetLight Data questions why governments need so much real-time data, and argues that de-identified historical data serves planning. Ger Baron, CTO of Amsterdam, describes querying a platform's data only when there is a suspicion, as the city does with holiday-rental platforms, instead of collecting everything. Simon Hania, DPO at Uber, warns that permits demanding fine-grained location data treat personal data as mere vehicle data. Technical specifications, he adds, could limit freedom of movement without democratic debate.
Moderator, Future of Privacy Forum & Dublin City University Event, Dublin/Brussels, 2020
Jules Polonetsky and Edoardo Celeste open the first joint webinar of the Future of Privacy Forum and Dublin City University on the independent DPO under the GDPR. In the first panel, Gabriela Zanfir-Fortuna asks regulators from Ireland, the Czech Republic, Belgium, and France what makes a DPO effective. Hielke Hijmans explains the Belgian DPA's April 2020 decision. A DPO who was also head of compliance, risk, and audit ended up advising on his own work. Hijmans wants the DPO to be a senior insider with some distance from day-to-day decisions. Rob van Eijk and Edoardo Celeste moderate the second panel with DPOs from Fort Privacy, Dropbox, Twitter, and Dutch Railways. They discuss how to be involved early without approving processing, whether one person can be both CPO and DPO, escalation to the board, and how outsourced DPOs stay involved.
Brenda Leong and Rob van Eijk of the Future of Privacy Forum host the eighth and final session of the Digital Data Flows Masterclass, on blockchain. Jake van der Laan of New Brunswick's Financial and Consumer Services Commission explains the technical basics through Bitcoin: an append-only transaction log, cryptographic hash functions that chain blocks together, proof-of-work consensus, and smart contracts on Ethereum. Matthias Artzt of Deutsche Bank then maps blockchain actors onto GDPR roles. Miners, nodes, and developers are neither controllers nor processors, he argues, while users may fall under the household exemption and governance bodies of private chains can be controllers. Because nobody can change data once it is on the chain, rectification and erasure are hard. Artzt reads erasure broadly as putting data beyond use and proposes "hashing out", which keeps personal data off-chain and stores only a hash on-chain. Once the controller deletes the off-chain data, the hash no longer points to anyone.
Rob van Eijk of the Future of Privacy Forum hosts a Digital Data Flows Masterclass on machine learning and speech, with Sara Jordan and Brenda Leong. Marine Carpuat of the University of Maryland explains neural machine translation and why semi-supervised techniques such as back-translation matter when paired training data is scarce. Her research focuses on "fluently inadequate" translations. These errors are rare but look plausible, as when a system translated a Facebook post as "attack them" and the police arrested its author. In the Q&A she admits that the research community has not seriously addressed removing data from trained models under rules such as the GDPR. Prem Natarajan of Amazon Alexa AI describes how conversational AI works. He presents semi-supervised learning, active learning, transfer learning, and self-learning as a path to less labelled data and less human review of recordings. Carpuat closes with the point that personalisation will make privacy questions more pressing.
Rob van Eijk gives the first part of an IAB Nederland webinar on understanding adtech, moderated by Tim Geenen of LiveRamp, IAB Nederland board member for privacy. Van Eijk explains the browser's components, rendering engines, and storage options. He takes apart two display ads to show the images, scripts, and third-party calls behind them. He maps the real-time bidding ecosystem, the identifiers in bid requests, and his measurements of third-party connections on newspaper sites across Europe. He shows browser fingerprinting with canvas, fonts, and audio, and how the default protections in Chrome, Firefox, and Safari differ. In the Q&A he covers cookie audits, including social sharing widgets that sites wrongly label as functional, tracking in apps, the Dutch exemption for low-impact analytics cookies, and the consent requirements of Planet49. Time ran out before the planned walkthrough of consent banners, which became the second session.
In the second IAB Nederland adtech webinar, moderated by Tim Geenen of the IAB Nederland board, Rob van Eijk of the Future of Privacy Forum moves from mechanics to consent. He revisits his measurements of third-party calls on European newspaper sites. Audience measurement under the Dutch analytics exemption, he explains, needs a processor agreement behind it. He walks through the GDPR conditions for valid consent, the Planet49 ruling, and the open question of cookie walls, and explains how a complaint to a regulator differs from a tip. He then reviews real sites with developer tools. He finds requests to third parties before any choice, separate consent across one company's brand sites, and refusals that take several clicks. His main lesson is that withdrawing consent must be as easy as giving it. In between he points to de-identification techniques such as differential privacy as a promising direction.
Understanding Digital Data Flows, Washington, DC, 2020
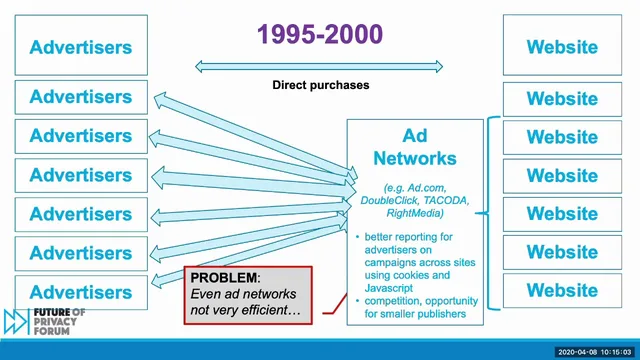
Christy Harris and Rob van Eijk of the Future of Privacy Forum give a webinar on the online advertising ecosystem in the Understanding Digital Data Flows series. Harris covers the basics: advertisers and publishers, first and third parties in the browser, cookies and pixels, supply-side and demand-side platforms, data management platforms and ad servers, and how companies recognise users across sites and devices. Van Eijk explains how browsers work, takes apart a display ad, and demonstrates fingerprinting. His graph measurements separate real-time bidding networks on newspaper sites in 27 European countries. He compares default tracking protections in Chrome, Firefox, and Safari. He then describes the end of third-party cookies: Google's Privacy Sandbox proposals such as FLoC, discussions in W3C groups, and the IAB's Project Rearc.
Angelique Carson hosts The Privacy Advisor Podcast with Rob van Eijk, who had just joined the Future of Privacy Forum as Managing Director for Europe after nearly ten years at the Dutch Data Protection Authority. There he represented European data protection authorities in the W3C negotiations on Do Not Track. They discuss why Do Not Track failed and what has to change for online advertising to thrive. He also describes what it is like to work as a technologist inside a data protection authority.
Cecile Schut of the Dutch Data Protection Authority and Rob van Eijk, a dual PhD candidate at Leiden University, share their experiences of the Dual PhD Centre programme. Van Eijk explains his motivation for in-depth research on measuring privacy in digital contexts and the technology behind online advertising. Schut gives the employer's view. Deep in-house expertise is a core value of the Authority, she says, and the Authority needs to be able to show that expertise to the outside world. The interview covers the programme's support, including research methodology training in the first year, a weekly peer group, close supervision, and an evaluation every six months.
FPF Book Club, Future of Privacy Forum, Washington, DC, 2019
Jules Polonetsky of FPF hosts a book club with Henry Farrell of George Washington University on Of Privacy and Power, written with Abraham Newman. Farrell describes the transatlantic conflict as a contest between cross-national coalitions, with security officials on both sides facing civil liberties advocates and data protection authorities. He sees Max Schrems using the Snowden revelations to bring down Safe Harbor, and the CJEU using such cases to expand its authority. Rob van Eijk, who joined the Dutch DPA in 2010, says the book showed him the bigger picture he had seen through a keyhole. He asks which cases could come next and what DPA guidance is still worth. Gabriela Zanfir-Fortuna points to the shared 1970s roots of US and European rules.
On the day he defended his PhD at Leiden University, 29 January 2019, Rob van Eijk speaks to NOS journalist Joost Schellevis on the NOS Radio 1 Journaal about the hidden side of online advertising. In real-time bidding, an auction sets the price of an ad slot in a fraction of a second, partly based on who is visiting. A few years ago, he says, tens of companies were watching while you surf. Now there are hundreds, and his research shows thousands of companies active in this market.
Stacey Gray of the Future of Privacy Forum moderates a Digital Data Flows Masterclass on online advertising technologies. Adam Towvim of Brandeis University's business school traces the move from direct media buying to programmatic advertising. He explains how advertisers, publishers, and intermediaries use cookies, pixels, hashed emails, and cross-device linking, and answers questions on ad fraud. Rob van Eijk of Leiden University walks through the nine steps of real-time bidding, from the publisher's ad slot to the bid requests that go out to hundreds of partners, including deal IDs and header bidding. He presents his graph-based research that separates real-time bidding networks on European news sites. In the open Q&A the speakers discuss why notice and consent is hard when nobody knows the bidders in advance, and how identity resolution links identifiers across devices.
Computers, Privacy & Data Protection Conference (CPDP2018), Brussels
ENISA organises this CPDP 2018 panel, chaired by Athena Bourka and moderated by Kai Rannenberg of Goethe University Frankfurt. It asks how technology can protect users against tracking and profiling across devices and apps, in line with the GDPR and the proposed ePrivacy Regulation. The speakers are Rob van Eijk of Leiden University, Mike O'Neill of BayCloud, Diego Naranjo of EDRi, and Fenneke Buskermolen of the European Commission. The panel covers the main techniques for online and mobile tracking, how privacy by design can help, and best practices for preventing tracking and obtaining consent.
Moderator, Computers, Privacy & Data Protection Conference (CPDP2016), Brussels
Frederik Zuiderveen Borgesius of IViR chairs and Rob van Eijk of the Dutch Data Protection Authority moderates a CPDP 2016 panel on the Norwegian DPA's report The Great Data Race. Bjørn Erik Thon of the Norwegian DPA presents the report, which covers tracking through cookies and logins, real-time bidding, and profiling. Users face take-it-or-leave-it choices, he argues, and he cites a survey in which most Norwegians are uncomfortable with targeted advertising. Townsend Feehan of IAB Europe argues that online advertising funds media diversity and warns that the GDPR will hit European intermediaries harder than large platforms. Paying for content, she says, is the alternative. Marie-Charlotte Roques-Bonnet of Microsoft describes interest-based advertising, the Windows 10 advertising ID and telemetry settings, and a shorter privacy statement after review by the Article 29 Working Party. Monique Goyens of BEUC criticises the information asymmetry and calls for DPA enforcement, privacy by design, and privacy by default.
Moderator, Computers, Privacy & Data Protection Conference (CPDP2015), Brussels
Rob van Eijk of the Dutch Data Protection Authority moderates an EDPS panel at CPDP 2015 on the Internet Privacy Engineering Network (IPEN). Achim Klabunde of the EDPS explains that IPEN started after the 2013 surveillance revelations and describes the action points from its Berlin workshop. Hannes Tschofenig traces where privacy can fail across crypto, standards, implementation, and deployment, and presents the IAB's privacy considerations for internet protocols. Simon Rice of the UK ICO says that many breaches come from basic failures such as unpatched software and SQL injection. Florian Stahl presents the OWASP Top 10 Privacy Risks for web applications. Marit Hansen of ULD adds unlinkability, transparency, and intervenability to the classic security goals. Jaap-Henk Hoepman of Radboud University presents privacy design strategies and patterns and a cookbook for developers. In the Q&A the panellists stress education and closer work between engineers, lawyers, and social scientists.
MEP Amelia Andersdotter chairs a European Parliament event on whether self-regulation is enough for Do Not Track. Robert Madelin of DG CONNECT calls tracking creepy and a risk to the information base of democracy, and argues that self-regulation can work if it is accountable. Rob van Eijk of the Dutch DPA, who represented the Article 29 Working Party in the W3C, states that in the EU Do Not Track means do not collect without consent. He urges industry to innovate with user-centric design. Nicolas Dubois of DG Justice, standing in for Paul Nemitz, explains how the data protection reform handles tracking through the right to object and codes of conduct. Stuart Hamilton of IFLA raises e-readers that monitor reading habits. Justin Brookman of CDT and Walter van Holst of EDRi question whether the narrow W3C standard can deliver what EU law requires.
Achim Klabunde of the EDPS moderates the first panel of the IPEN Workshop 2014, on the gaps between existing privacy tools and what people need. Florian Stahl and Stefan Burgmair present the OWASP Top 10 Privacy Risks for web applications. Hannes Tschofenig of ARM explains how the IETF and the W3C build privacy considerations into standards. Jens Kubieziel traces how Tor evolved, including its defences against censorship. Joss Wright of the Oxford Internet Institute notes that privacy keeps moving up the development stack and that academic cryptography rarely reaches products. Stéphane Petitcolas of the CNIL shows what mobile apps leak in practice. Rob van Eijk of the Dutch DPA frames privacy as a fundamental right shaped by purpose and context. Most data flows, he notes, happen beyond the device and out of view.
This NOS video item from July 2013 is about real-time bidding. Advertisers trade personal data worldwide as a matter of course, the item says, and real-time bidding now does it in a fraction of a second, with a Dutch company leading the way.
In an NOS item from July 2013, Rob van Eijk, then doing PhD research at Leiden University on online tracking, explains how real-time bidding has grown and why it will keep growing.
Christine Runnegar of ISOC and Sophie Kwasny of the Council of Europe co-moderate an IGF 2012 workshop on tracking the trackers. Rob van Eijk, a PhD student at Leiden University who represents the Article 29 Working Party in the W3C Do Not Track debate, explains that unique identifiers, from cookies to browser fingerprints, are the core of tracking. The European position, he says, is "do not collect" without consent. Wendy Seltzer of the W3C describes the Do Not Track standard in progress. Cornelia Kutterer of Microsoft explains why Internet Explorer 10 sends Do Not Track by default. Kimon Zorbas of IAB Europe calls that default paternalistic and argues that limits on behavioural advertising favour large platforms. Malavika Jayaram of CIS India describes Indian rules that make cyber cafés identify and log their users.
Future of Privacy Forum De-identification Workshop Day, Washington DC, 2011
David Hoffman of Intel moderates the closing panel of a Future of Privacy Forum workshop on what re-identification research means for the law. Daniel Solove of George Washington University Law School presents PII 2.0, which treats identifiability as a continuum of risk and applies fewer Fair Information Practices as the risk falls. Jane Yakowitz of Brooklyn Law School argues that the value of public research data outweighs realistic re-identification risks. She proposes a safe harbour for data producers who apply basic anonymisation, and penalties for recipients who re-identify. Harley Geiger of CDT turns to health data and cautions that a ban on re-identification would hamper security research. Rob van Eijk of the Dutch DPA, speaking for himself, treats re-identification as further processing that needs a legal ground. He proposes managing privacy risk like security risk. The discussion turns to First Amendment limits on penalising re-identification.